_protection. confidence.
we help you build them all.
A single-agent, cloud-native security platform engineered for modern businesses and the MSPs who safeguard them against ever-changing cyber threats.
_why do we do it?
"We believe every business deserves a shield."
Todyl replaces fragmented point products with an all-in-one architecture. Deploy SASE, ZTNA, MXDR, SIEM, and EDR through a single lightweight agent (SGN Agent) and a unified cloud management console.
Straightforward, powerful cybersecurity designed to prevent catastrophic risk without overwhelming limited IT resources.
Multi-tenant visibility, automated operations, and co-managed 24/7 MXDR to build customer trust and safeguard margins.
_1. Secure Global Network™ (SGN) – Cloud Network & SASE
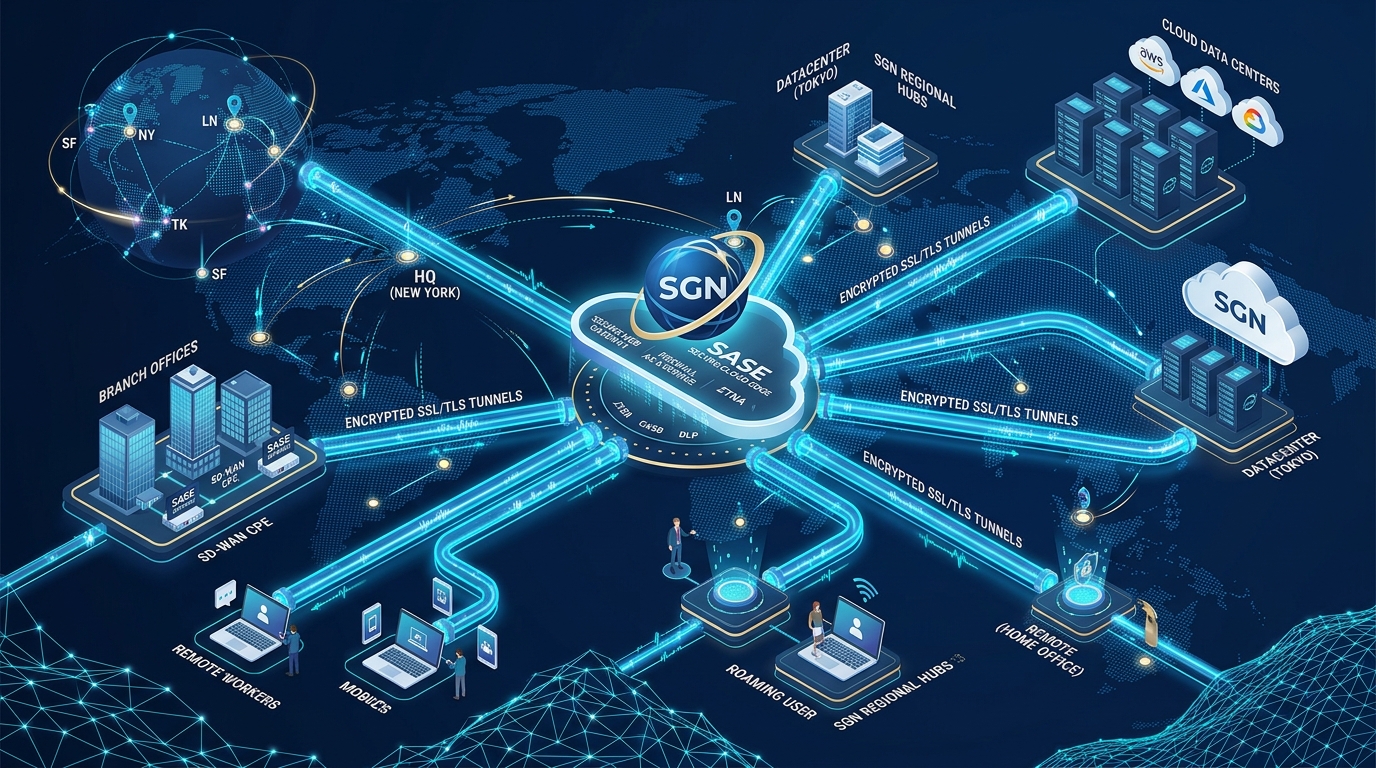
The fundamental backbone connecting remote workers, branch offices, cloud resources (AWS/Azure), and on-premise data centers into a single encrypted cloud network.
🔗 1.1. Network Connection and Tunnel Parameters:
- User-to-Cloud Tunnel: Direct device-based secure connection with SGN Agent.
- Site-to-Cloud Tunnel: IPSec / WireGuard-based branch/office tunnels (connecting without altering physical firewalls).
- Cloud-to-Cloud Tunnel: High-speed BGP / Peering integration with AWS, Azure, Google Cloud, and private VDC infrastructures.
⚡ 1.2. Performance and Architecture:
- Smart Routing: Low-latency routing to the nearest PoP (Point of Presence) location worldwide.
- Bandwidth Management: Traffic prioritization (QoS) and line backup between branches.
_2. Zero Trust Network Access (ZTNA) – Access Management
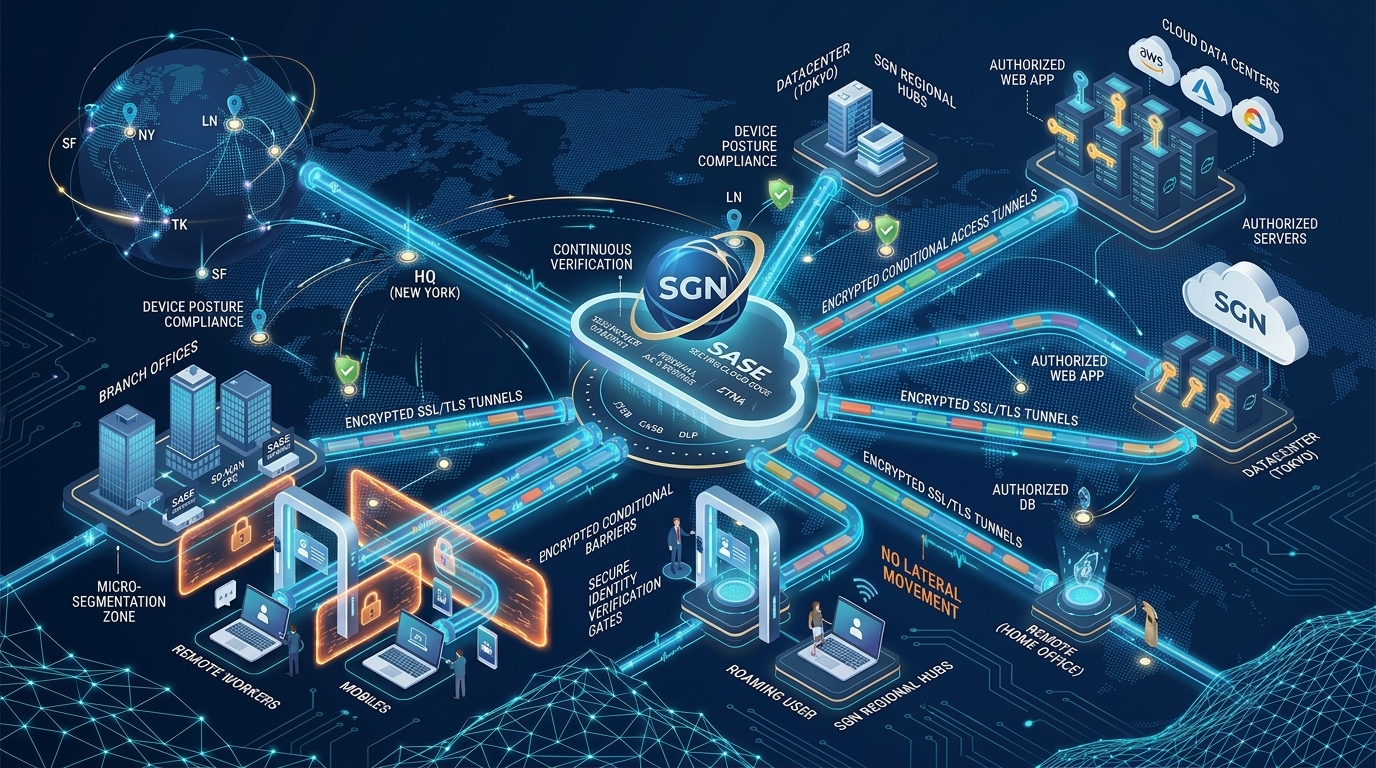
Eliminates the vulnerable "whoever enters the network accesses everywhere" concept of legacy VPNs, enforcing strict least-privilege verification.
⚙️ 2.1. Conditional Access Policies:
- Identity-Aware Access: Azure AD / Okta / Google Workspace integration with role/group-based granular authorization.
- Device Posture Check: Dynamic access grants based on EDR status, OS patch level, and device compliance posture.
🛡️ 2.2. Micro-Segmentation Rules:
- IP / Port / Protocol Restriction: Routing users only to specific authorized ports (e.g. 192.168.1.50:3389) rather than broad subnets.
- Lateral Movement Prevention: Complete endpoint isolation stopping lateral propagation of cyber threats across workstations.
_3. Secure Web Gateway (SWG) & DNS Security
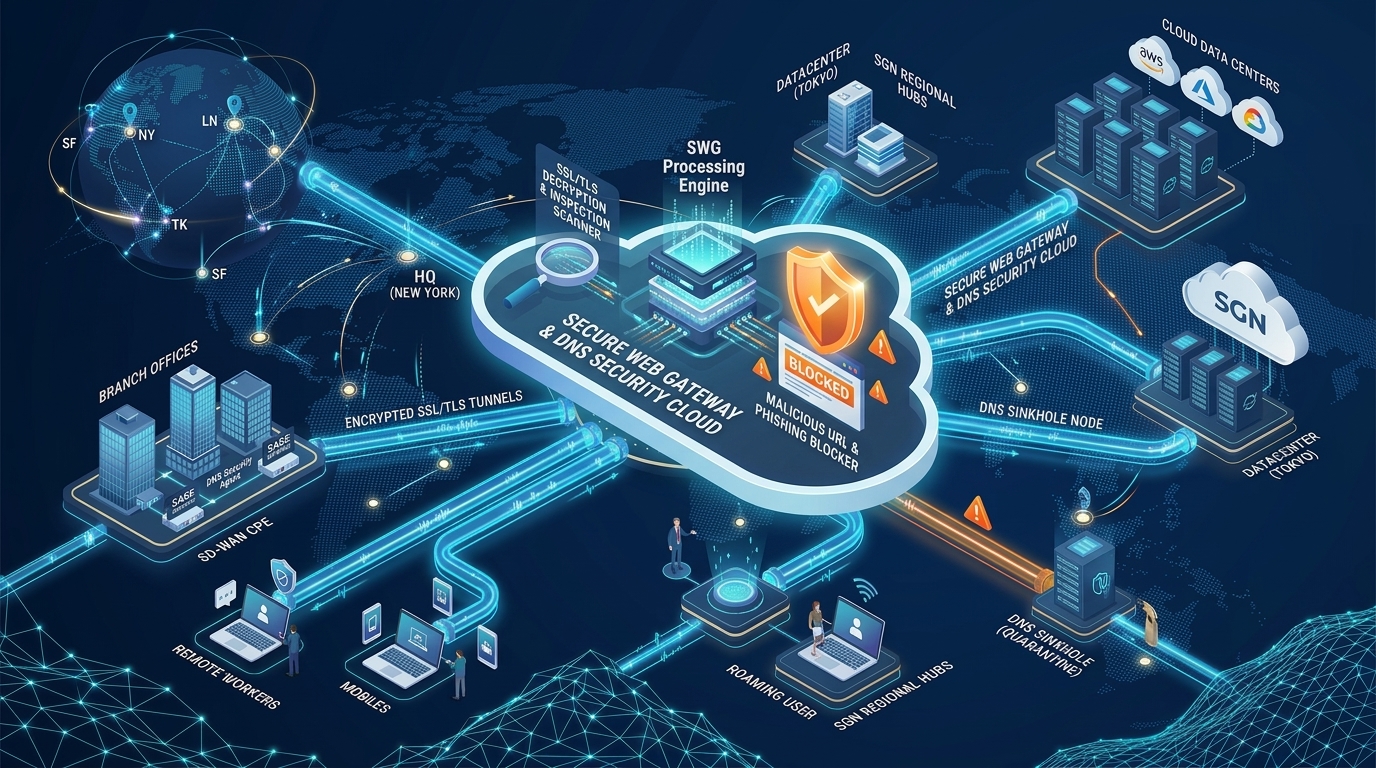
Real-time inspection of all outbound and inbound web traffic at the cloud edge, regardless of where or how users connect.
🌐 3.1. Web & Content Filtering:
- Category-Based Blocking: Automated blocking of phishing, adult, illegal, malware-hosting, or productivity-reducing sites.
- SafeSearch & Restrictions: Enforce strict corporate usage policies on search engines and streaming services.
🔍 3.2. Deep Traffic and Threat Inspection:
- SSL/TLS Decryption (SSL Inspection): High-performance HTTPS decryption to inspect encrypted payloads without bottlenecks.
- Phishing & Malicious URL Defense: Instant zero-hour protection with global threat intelligence.
- DNS Sinkholing: Redirecting malicious domain queries to secure isolation sinks.
_4. Cloud Next-Gen Firewall (NGFW) & CASB
Deep Layer 7 application visibility and policy enforcement across enterprise SaaS, cloud workloads, and physical networks.
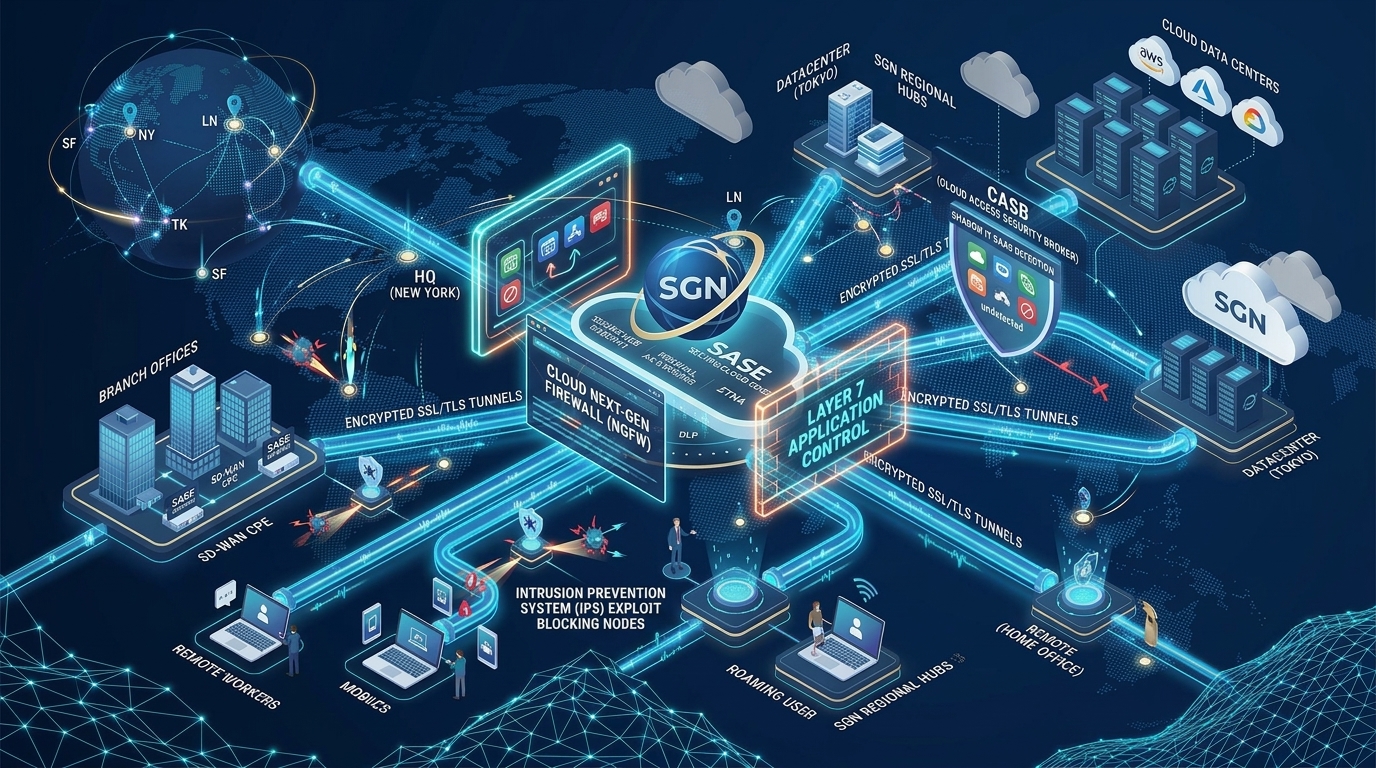
🎯 4.1. Layer 7 App Detection
Detecting and controlling non-standard port applications (Tor, BitTorrent, UltraSurf, P2P) regardless of port hopping.
☁️ 4.2. Shadow IT & CASB
Monitoring and restricting unsanctioned SaaS file uploads (Google Drive, WeTransfer, Dropbox) to prevent data exfiltration.
🛑 4.3. Cloud IPS Defense
Blocking network exploits, CVE vulnerability probes, and malicious brute-force scans right at the tunnel level.
_5. Endpoint Protection (EDR & NGAV)
Advanced behavioral AI protection integrated into the lightweight SGN agent across Windows, macOS, and Linux endpoints.
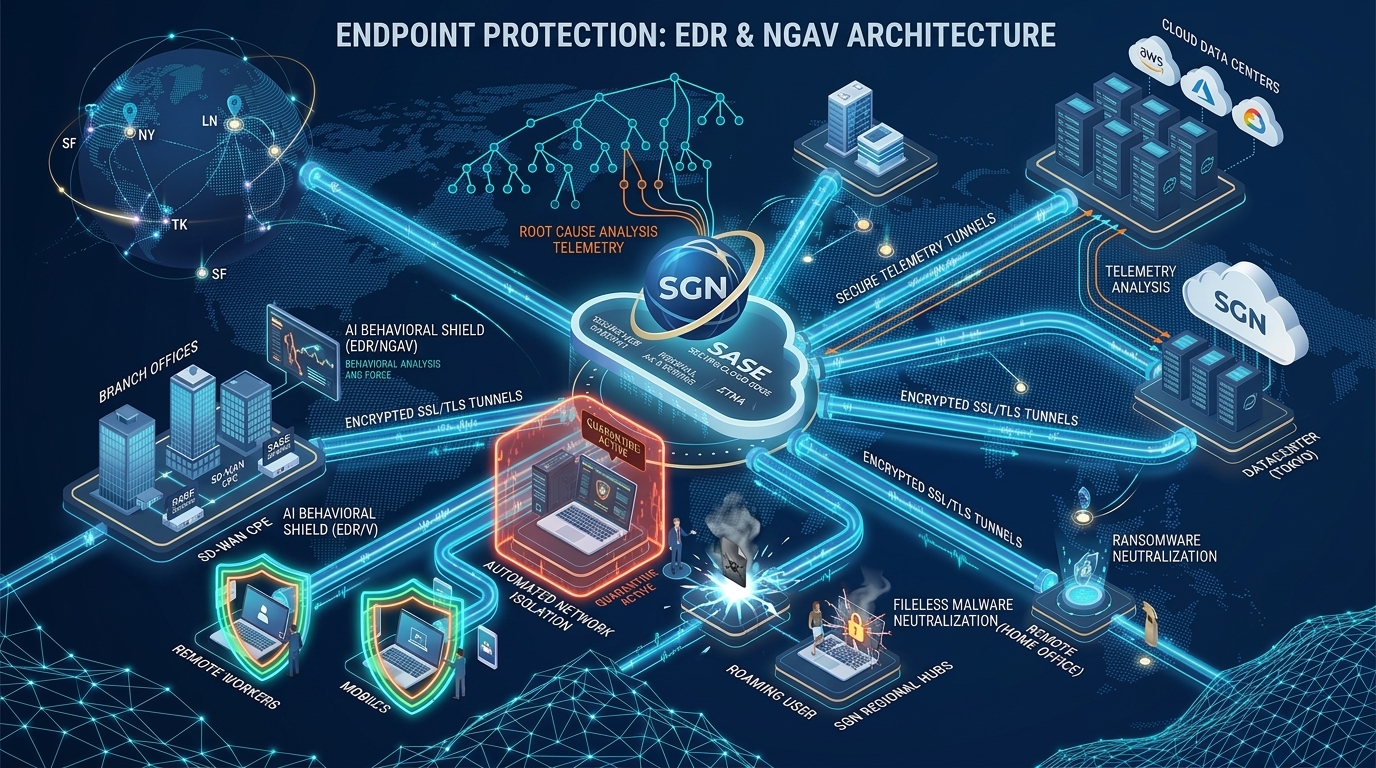
🛡️ 5.1. Next-Generation Antivirus (NGAV):
- Behavioral Engine: Intercepting zero-day attacks and ransomware variants based on heuristic behavior without waiting for signature updates.
- Fileless Malware Defense: Stopping stealth in-memory attacks executing via PowerShell, WMI, or living-off-the-land binaries.
🚨 5.2. EDR and Incident Response:
- Automated Network Isolation: Instantly quarantining compromised hosts from the local LAN while keeping the Todyl cloud management line open.
- Process Tree Telemetry: Root-cause analysis tracing malicious executions back to original scripts, parent processes, and network sockets.
_6. Managed Extended Detection & Response (MXDR)
Expert-led 24/7/365 threat monitoring and rapid response delivered seamlessly by Todyl SOC analysts in coordination with Bulutforce engineers.
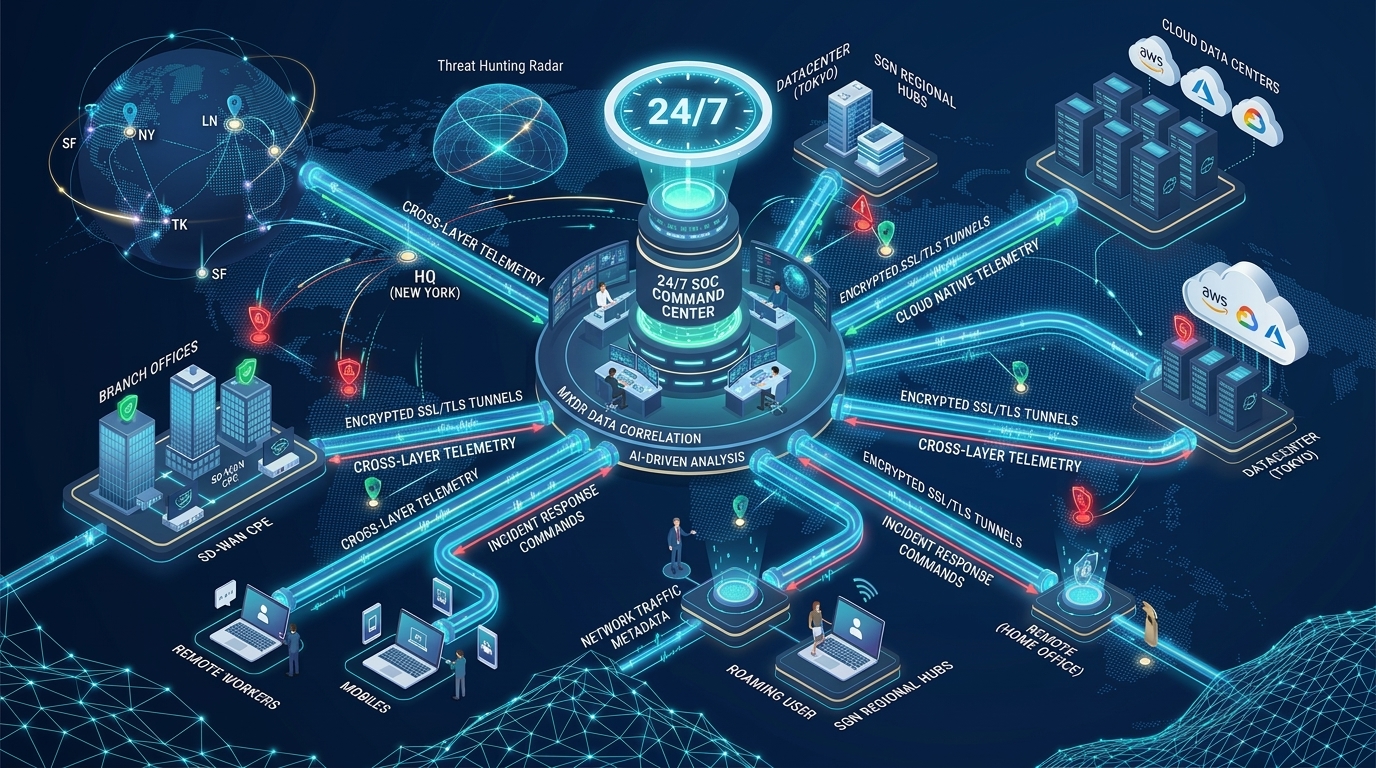
🏹 6.1. Continuous Threat Hunting:
- Cross-Layer Telemetry: Correlating SGN Network data + ZTNA Access patterns + EDR Endpoint telemetry into a single correlated XDR engine.
- Proactive Investigation: Uncovering hidden APT persistence before damages occur.
🛠️ 6.2. 24/7 Active Incident Mitigation:
- Analyst-Led Remediation: Todyl SOC experts apply defensive policies and isolate threats directly during off-hours.
- Bulutforce L2/L3 Turkish Support: Local incident coordination, root-cause forensics, and regulatory notifications.
_7. SIEM & Log Management
Scalable centralized logging, deep query analytics, and regulatory reporting tailored for stringent compliance frameworks.
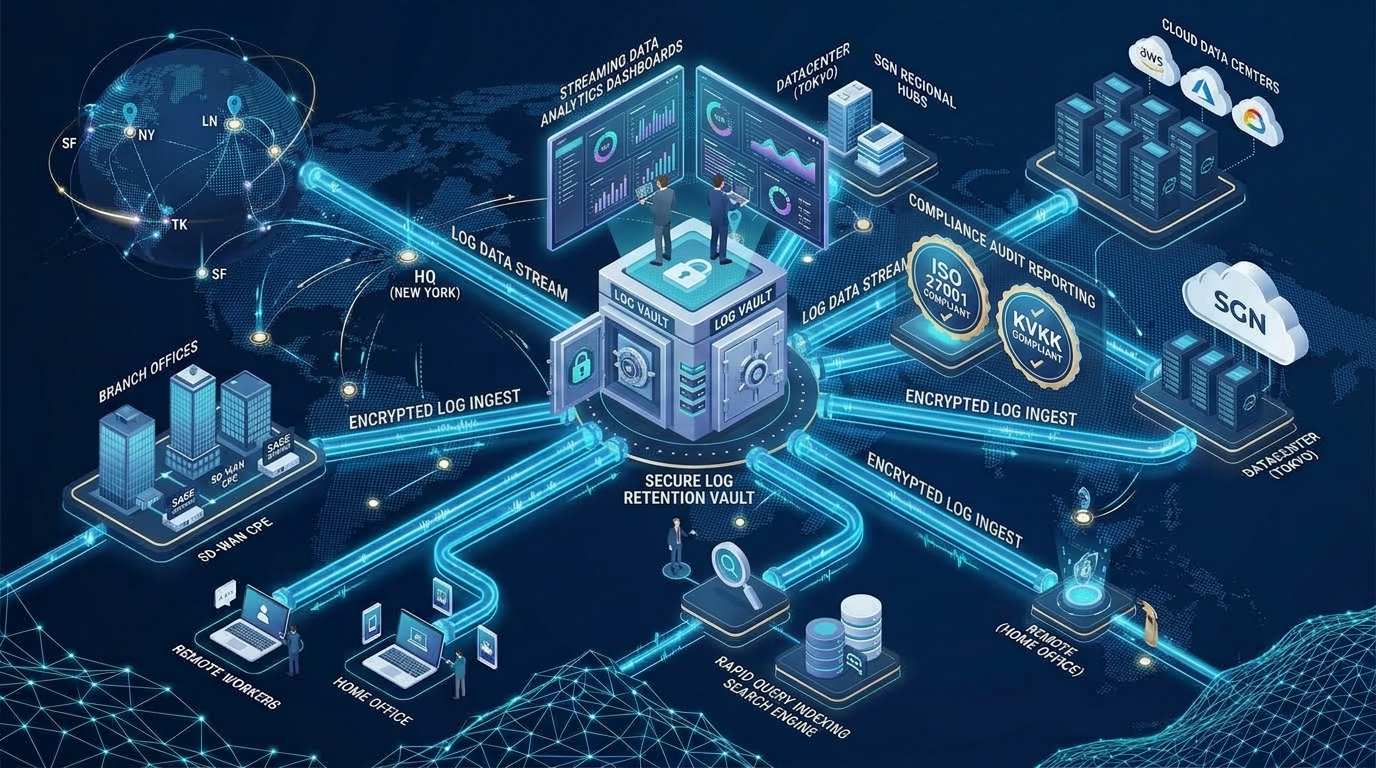
📦 7.1. Log Aggregation & Storage:
- Flexible Retention: Secure encrypted cloud retention of all SGN network flows, EDR alerts, and ZTNA access events.
- Instant Search: High-speed log exploration with custom query syntax for security audits.
📋 7.2. Compliance Frameworks:
- KVKK / ISO 27001 / BDDK Readiness: Pre-built reporting templates enabling one-click audit trail exports.
_8. Licensing and Module Matrix
Modular licensing architecture allowing businesses to start with essential SASE layers and seamlessly add advanced capabilities.
| _Service Module | _Core Function | _Metric / Unit |
|---|---|---|
| SGN / SASE | Cloud Network & Virtual Firewall | Per User / Device |
| ZTNA | Identity-Based Secure Access | Per User |
| SWG & DNS | Web & SSL Filtering | Per User / Device |
| NGFW & CASB | Layer 7 & Shadow IT Control | Per Network / Tunnel |
| EDR / NGAV | Behavioral Endpoint Protection | Per Device (Agent) |
| MXDR | 24/7 SOC & Threat Hunting | Per User / Device |
| SIEM & Log | Log Storage & Compliance Analytics | GB Volume / Per Device |
_navigation
8 MODULES _partner
_get started with todyl
Contact Bulutforce engineers for custom sizing, demo instances, and special pricing.